


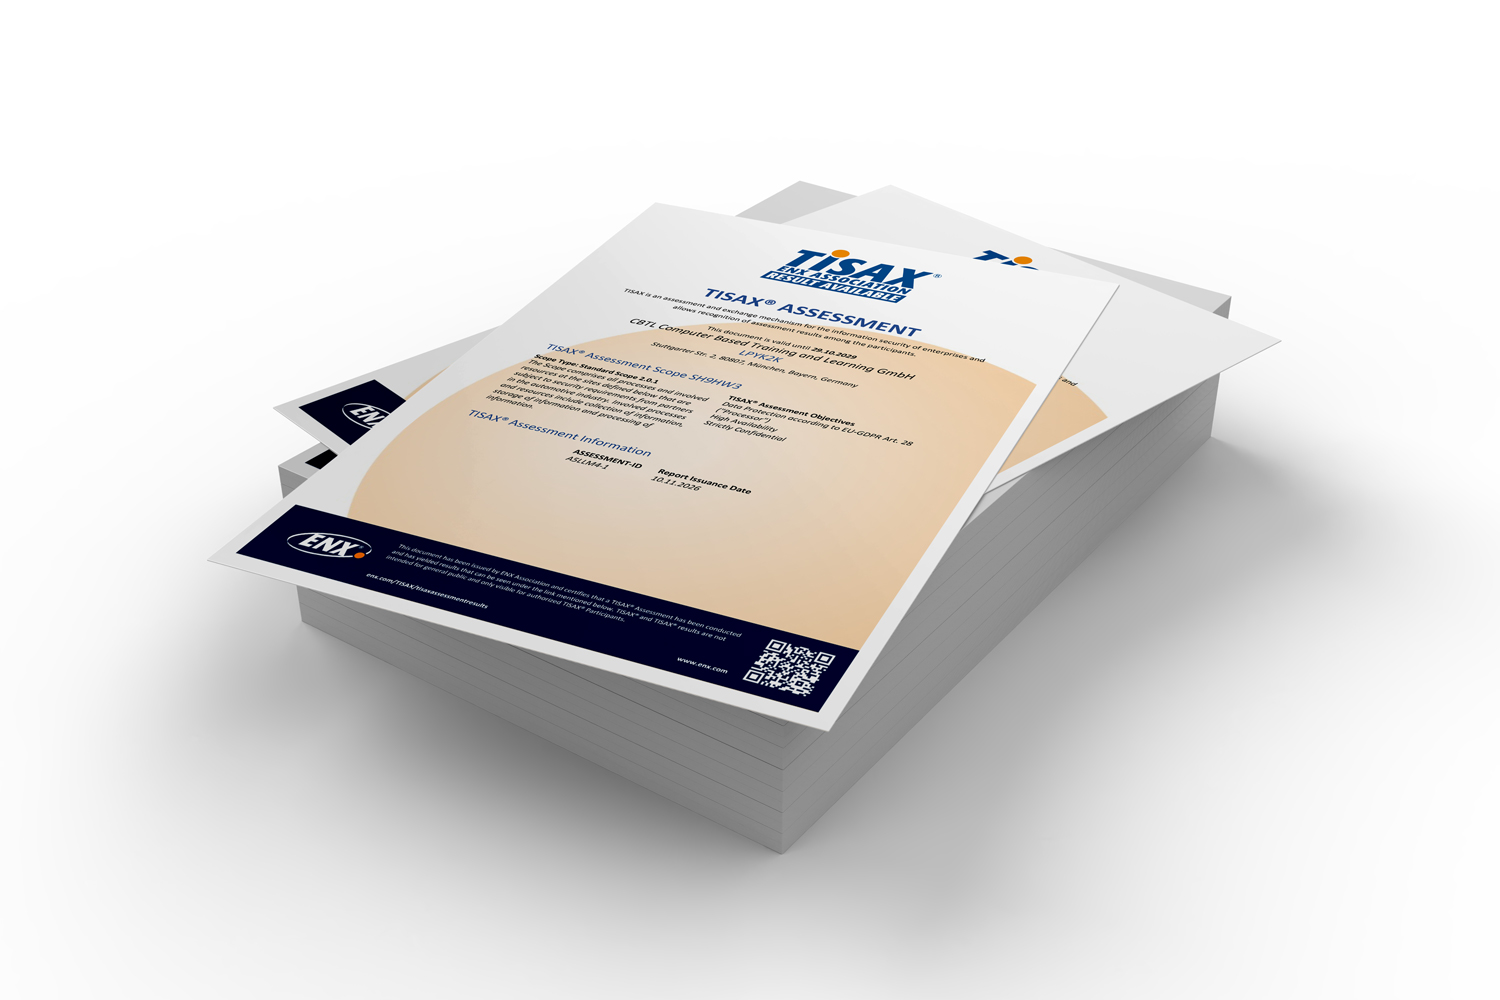

Information security is a fundamental prerequisite for trust and cooperation. We are pleased to announce that CBTL has successfully completed the TISAX® assessment for the third time.
We share our assessment results with our partners in the automotive industry via the TISAX (Trusted Information Security Assessment Exchange) mechanism. It can be verified via the Scope ID SH9HW3 on the ENX portal (https://portal.enx.com/).
TISAX participants can access their assessment results via this platform. Interested business partners can also request that we share our results directly with them.
An overview of the audited scope
The assessment covers all processes and resources at our sites that are subject to our partners’ security requirements. This explicitly includes the collection, storage and processing of information, including our EVOLUTION³ production platform.
Verified assessment objectives:
- Data protection in accordance with Article 28 of the EU GDPR (‘Data Processors’): The responsible handling of personal data on behalf of our clients.
- ‘High Availability’: Operations that minimise downtime and ensure the continuous provision of our services.
- ‘Strictly confidential’: The protection of particularly sensitive information belonging to our partners.
What is TISAX?
TISAX® (Trusted Information Security Assessment Exchange) is an assessment and exchange mechanism for information security within companies in the automotive industry. It was developed on the basis of the ‘Information Security Assessment’ (VDA ISA) catalogue published by the German Association of the Automotive Industry (VDA) and is operated by the ENX Association.
Unlike a traditional certificate, TISAX is the result of an audit carried out by an accredited audit provider. It is exchanged between participants via the ENX portal. This means that information security audits no longer need to be repeated for each individual partner, as a recognised result creates a binding standard and saves effort on both sides.
TISAX and ISO 27001 – what is the difference?
ISO/IEC 27001 is an international standard for information security management systems (ISMS). It enables certification by accredited bodies and is used across all sectors. TISAX, on the other hand, is a sector-specific mechanism within the automotive industry, based on the VDA-ISA catalogue.
The key difference lies in the objective and the outcome: with TISAX, there is no ‘certification’, but rather an assessment. The result is exchanged exclusively between participants via the ENX portal. In practice, there is considerable overlap in the requirements. Organisations with experience of ISO 27001 already meet many of the VDA-ISA requirements.
TISAX supplements this with sector-specific requirements and protection levels. For companies operating in the automotive sector, TISAX is generally the required proof of compliance. This applies regardless of whether the company holds additional ISO 27001 certification.
Note: TISAX® and the TISAX label are registered trademarks of the ENX Association. The results of a TISAX assessment are exchanged exclusively via the ENX portal amongst TISAX participants and are not issued publicly as a ‘certificate’.